A WAF stops attacks and AAM verifies identity. But the moment the HTML, JavaScript, session data and API responses of a sensitive application reach the user’s device, that data is exposed to client-side risks.
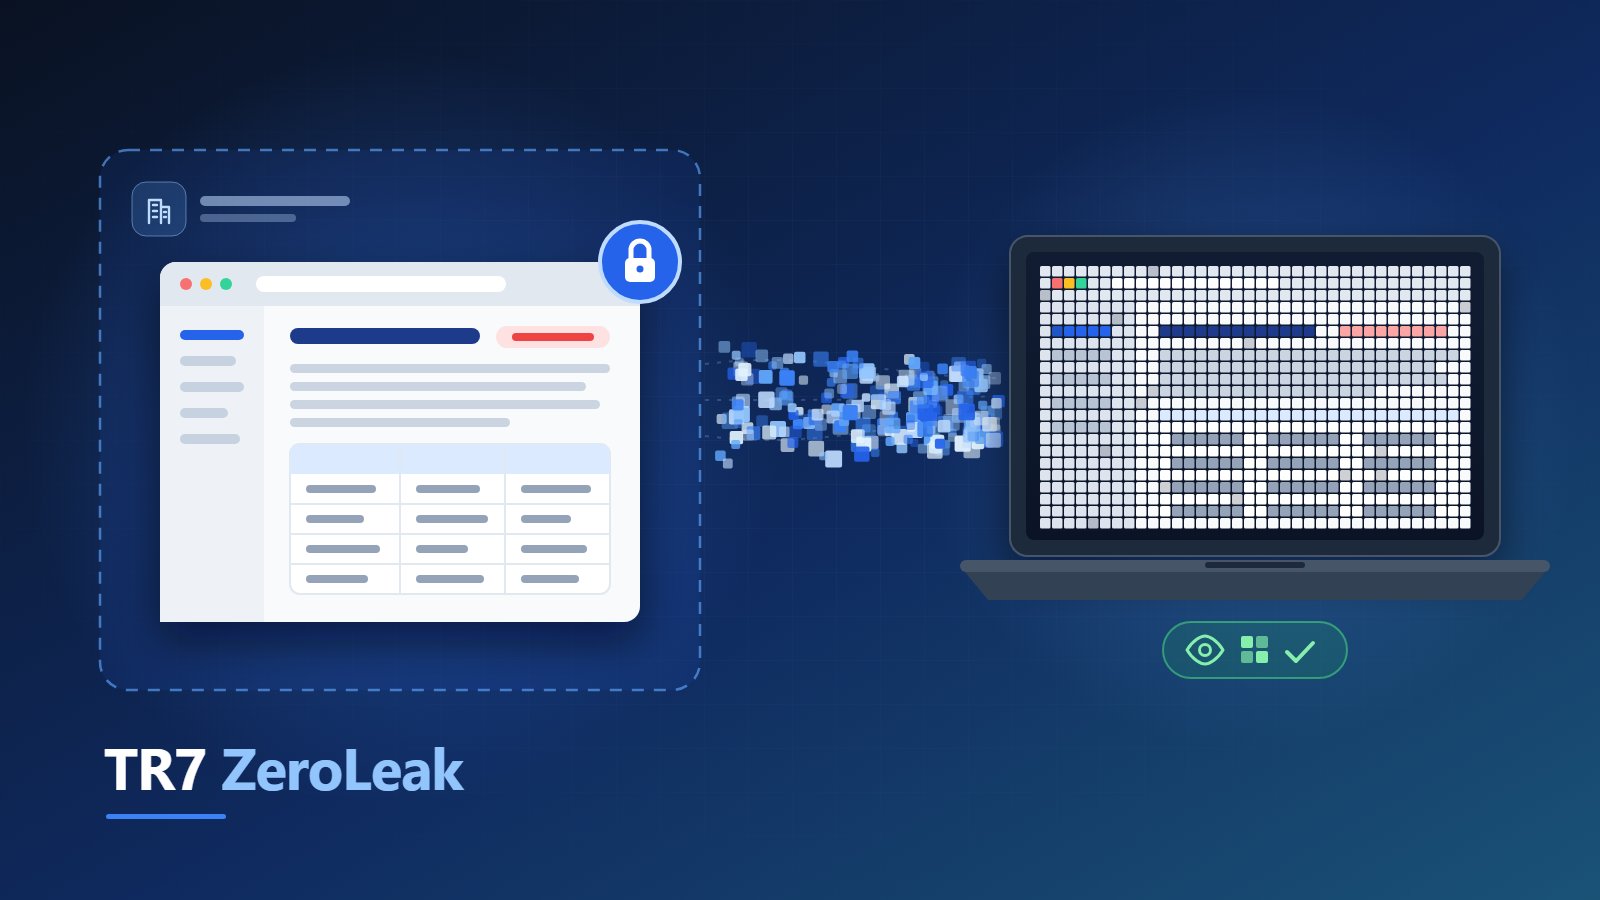
ZeroLeak closes this risk at the architecture level. The real web application runs inside your network in an isolated browser environment. Only a live pixel stream is sent to the user’s device, while keyboard and mouse input comes back through a controlled channel.
What ZeroLeak offers
- Pixels Only: HTML, JavaScript, API data and session info never reach the client.
- Anti-OCR: Visual protection against screenshots, screen recording and AI vision.
- Full Forensic: Every session traceable, recordable and replayable.
- On-Prem and Agentless: Runs inside your network; no agent installed on the user’s device.
ZeroLeak is offered as an add-on alongside TR7’s four products: ADC, WAAP, AAM and GTM. See the ZeroLeak page for details, and our blog post for an in-depth look at the architecture.